Oxford, England
ProjectsOngoing

Penetration testing consultancy

Penetration testing consultancy
Alongside my full-time DevSecOps role, I work as an independent penetration testing consultant. Testing systems from the attacker's side sharpens the defensive work I do every day. I also know the client's side of the table. For more than two years I've managed and delivered my employer's annual penetration testing programme: scoping each test, engaging vendors, and tracking remediation through to closure.
  • Agree scope and rules of engagement with the client before any testing begins
  • Carry out reconnaissance and OSINT to map the attack surface
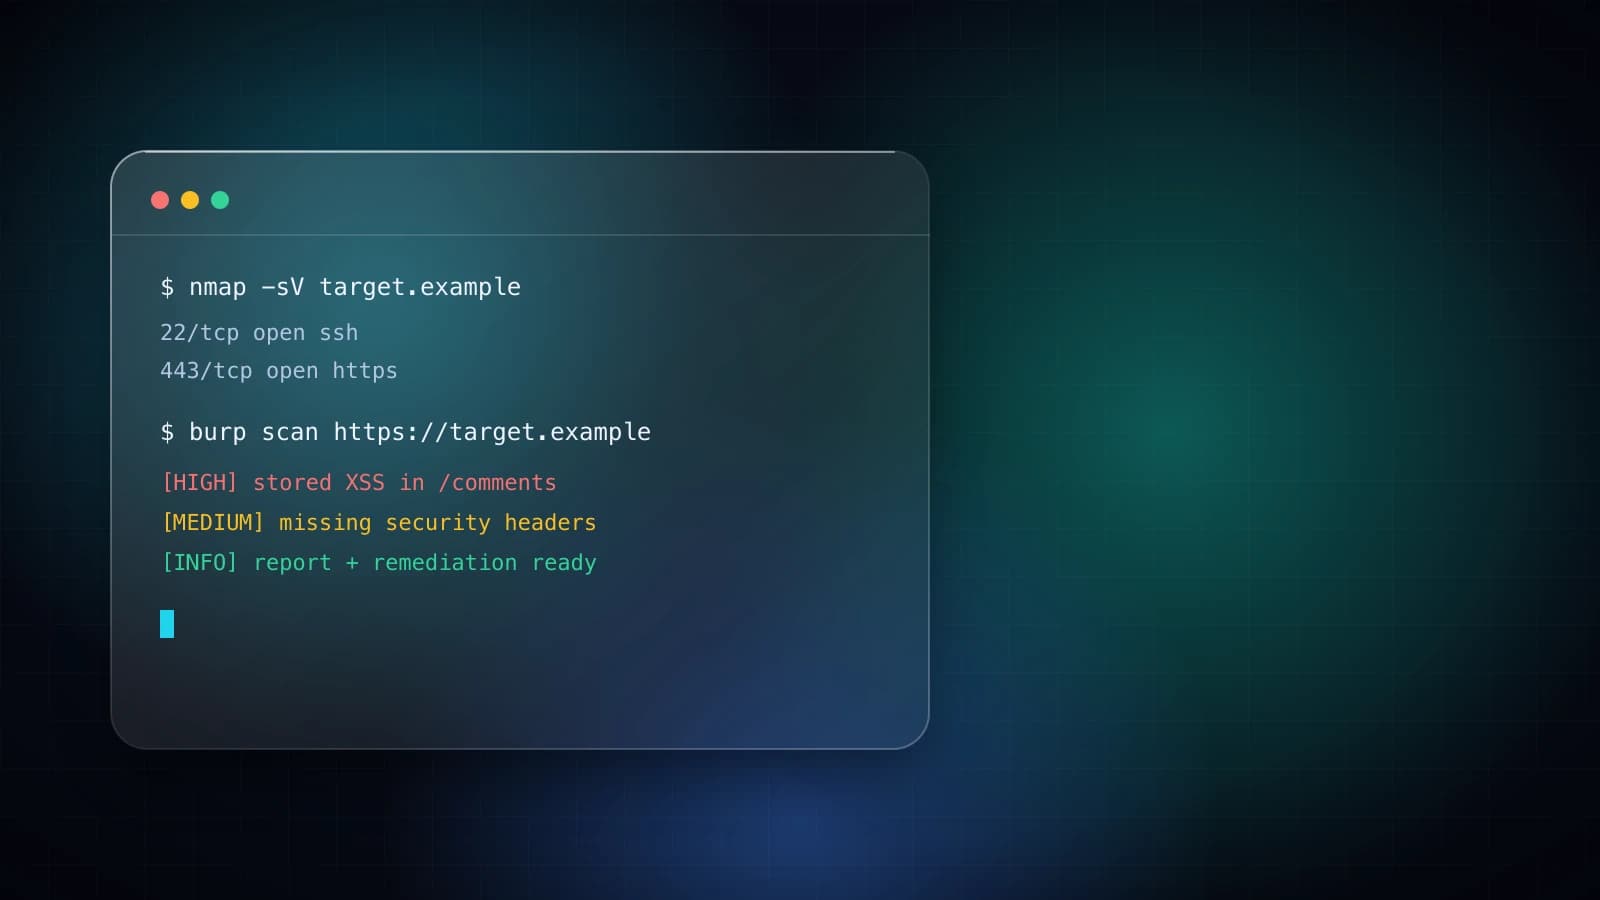
  • Run vulnerability scanning with Nessus and Nmap, then verify findings manually
  • Test web applications with Burp Suite, and WordPress sites with WPScan
  • Analyse traffic with Wireshark where the engagement calls for it
  • Report risk-rated findings in plain language, with practical remediation guidance
Kali Linux, Burp Suite, Nmap, Nessus, WPScan, Wireshark, OSINT Framework. Certified Ethical Hacker (CEH), EC-Council.

Related projects

Xcevia: a security consultancy in the making
In development

Xcevia: a security consultancy in the making

A practitioner-led security consultancy for UK SMEs that I'm building on the side. It's not trading yet. The groundwork is being laid for Cyber Essentials Plus readiness, cloud security, and DevSecOps support.
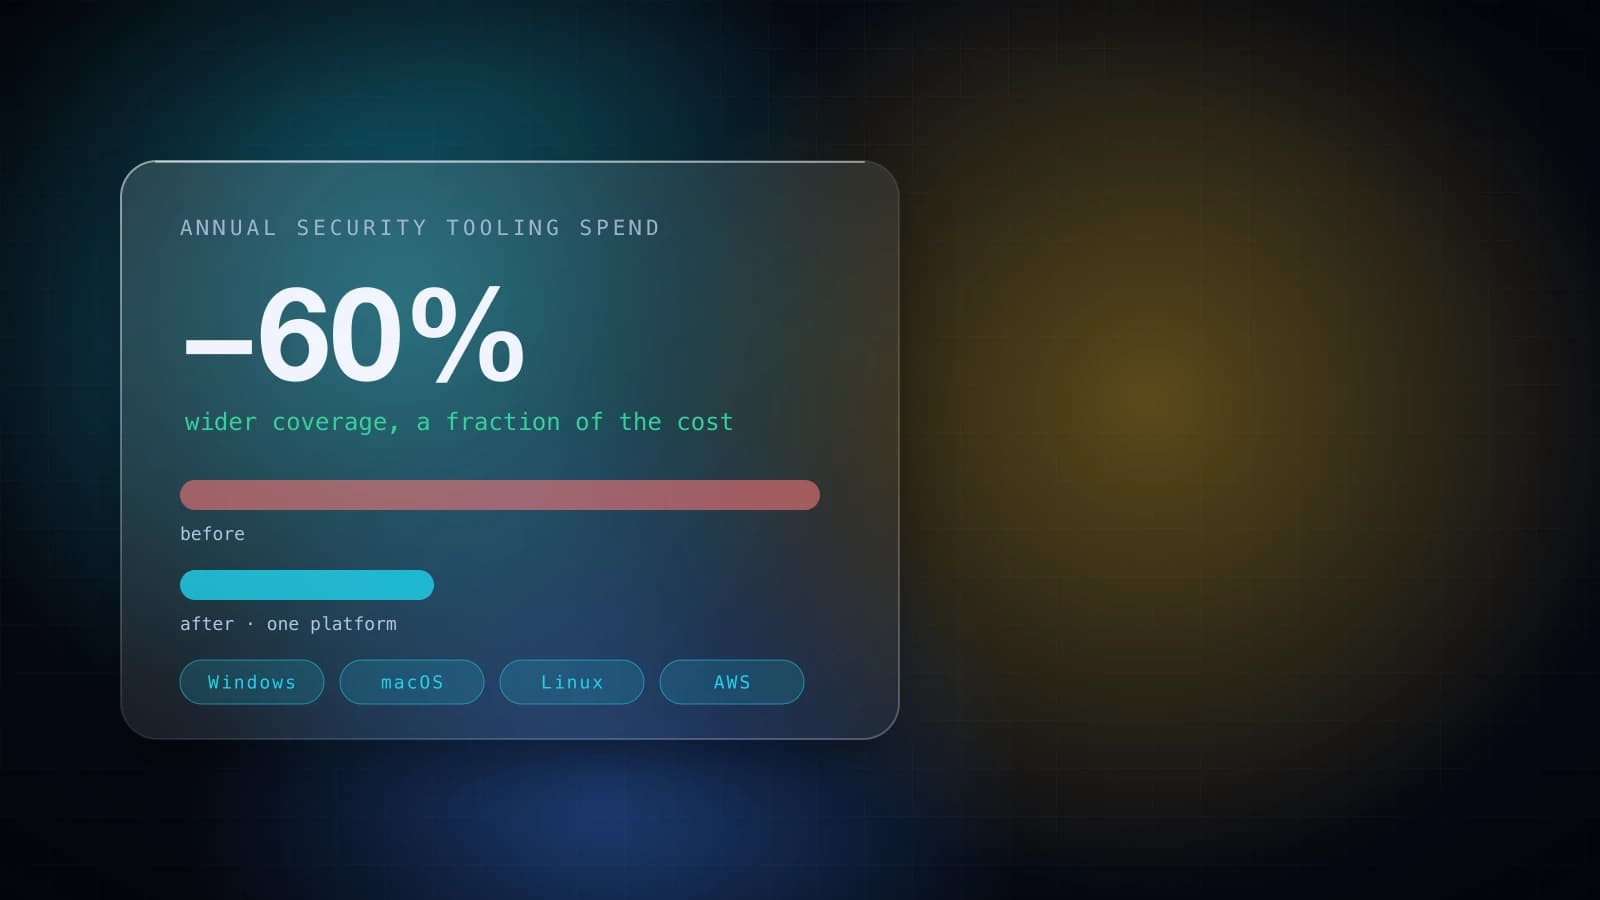
Cutting security tooling costs by 60% while widening coverage

Cutting security tooling costs by 60% while widening coverage

A vendor review at a UK health-tech company. I consolidated onto one platform that covers every operating system and the cloud, then closed the one remaining gap with a dedicated patch management tool.
Incident response and endpoint security in health tech

Incident response and endpoint security in health tech

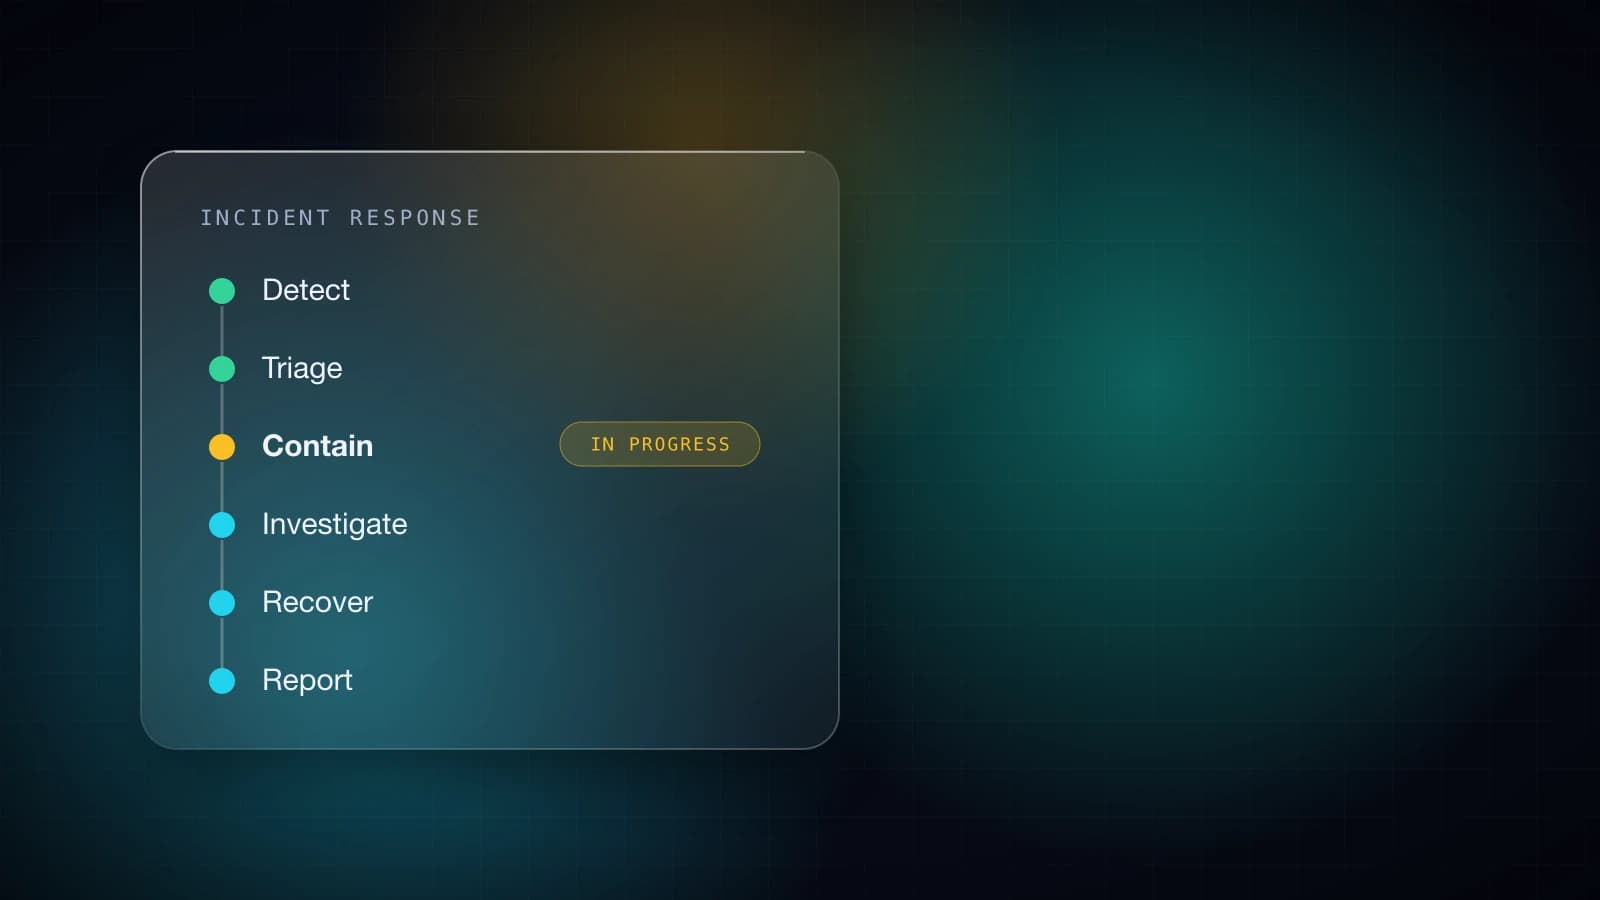
Owning day-to-day alert handling across a multi-OS estate at a UK health-tech company, correlating cloud activity with endpoint telemetry, and leading the response to a live, high-severity security incident.
Embedding SAST into CI/CD pipelines

Embedding SAST into CI/CD pipelines

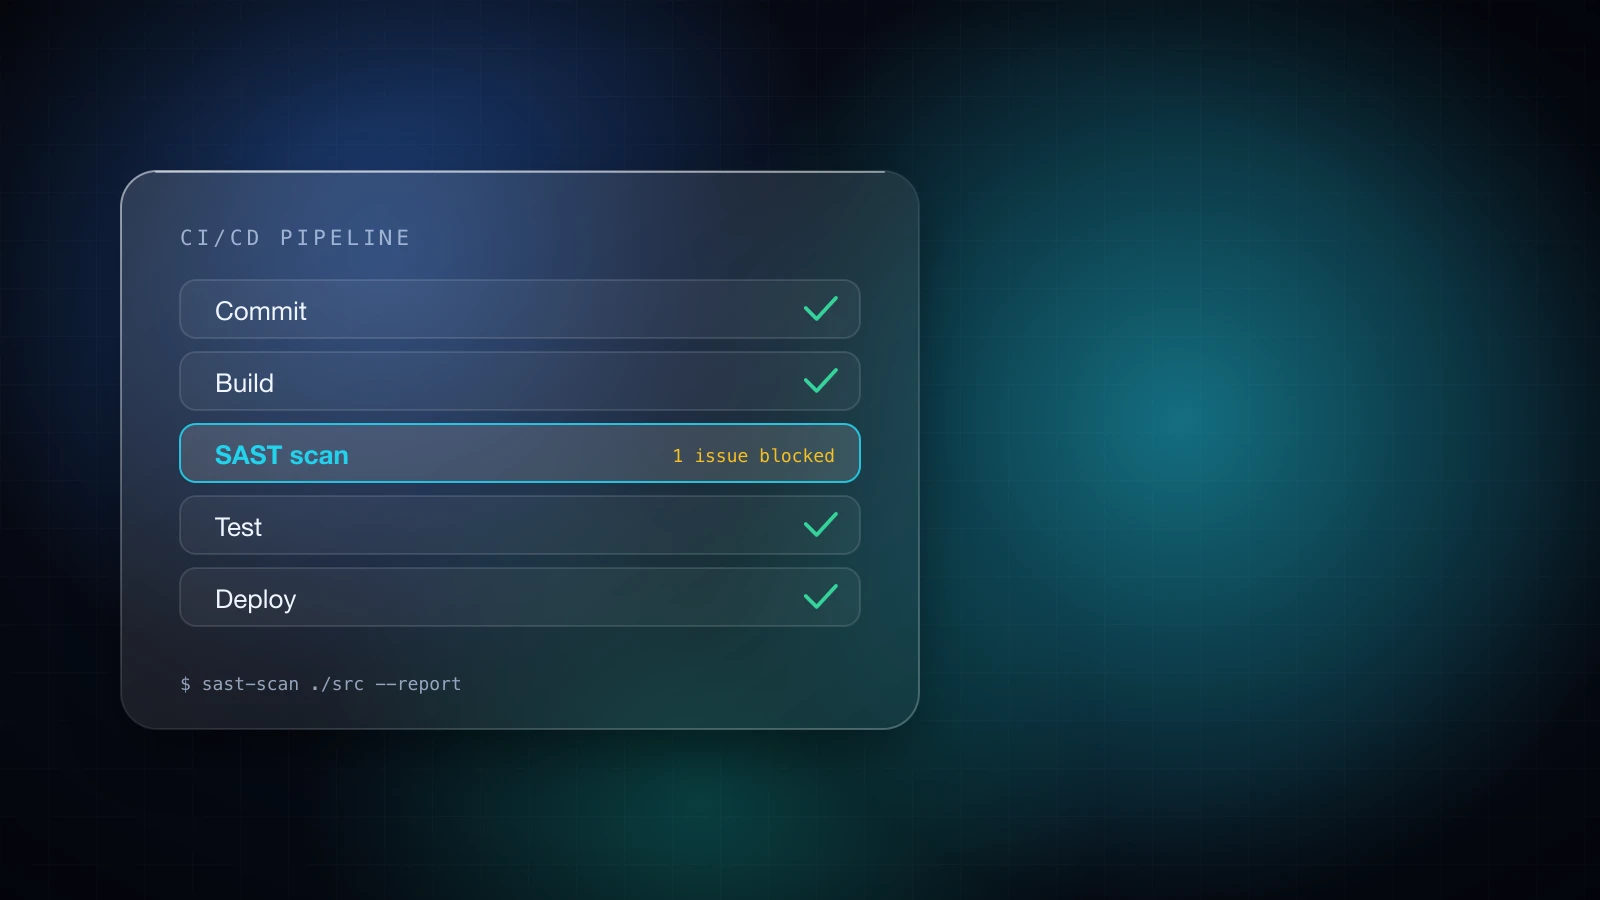
Adding static application security testing (SAST) to a health-tech company's delivery pipelines, so developers find code-level vulnerabilities before release rather than after.
Cyber Essentials Plus, ISO 27001 and security governance

Cyber Essentials Plus, ISO 27001 and security governance

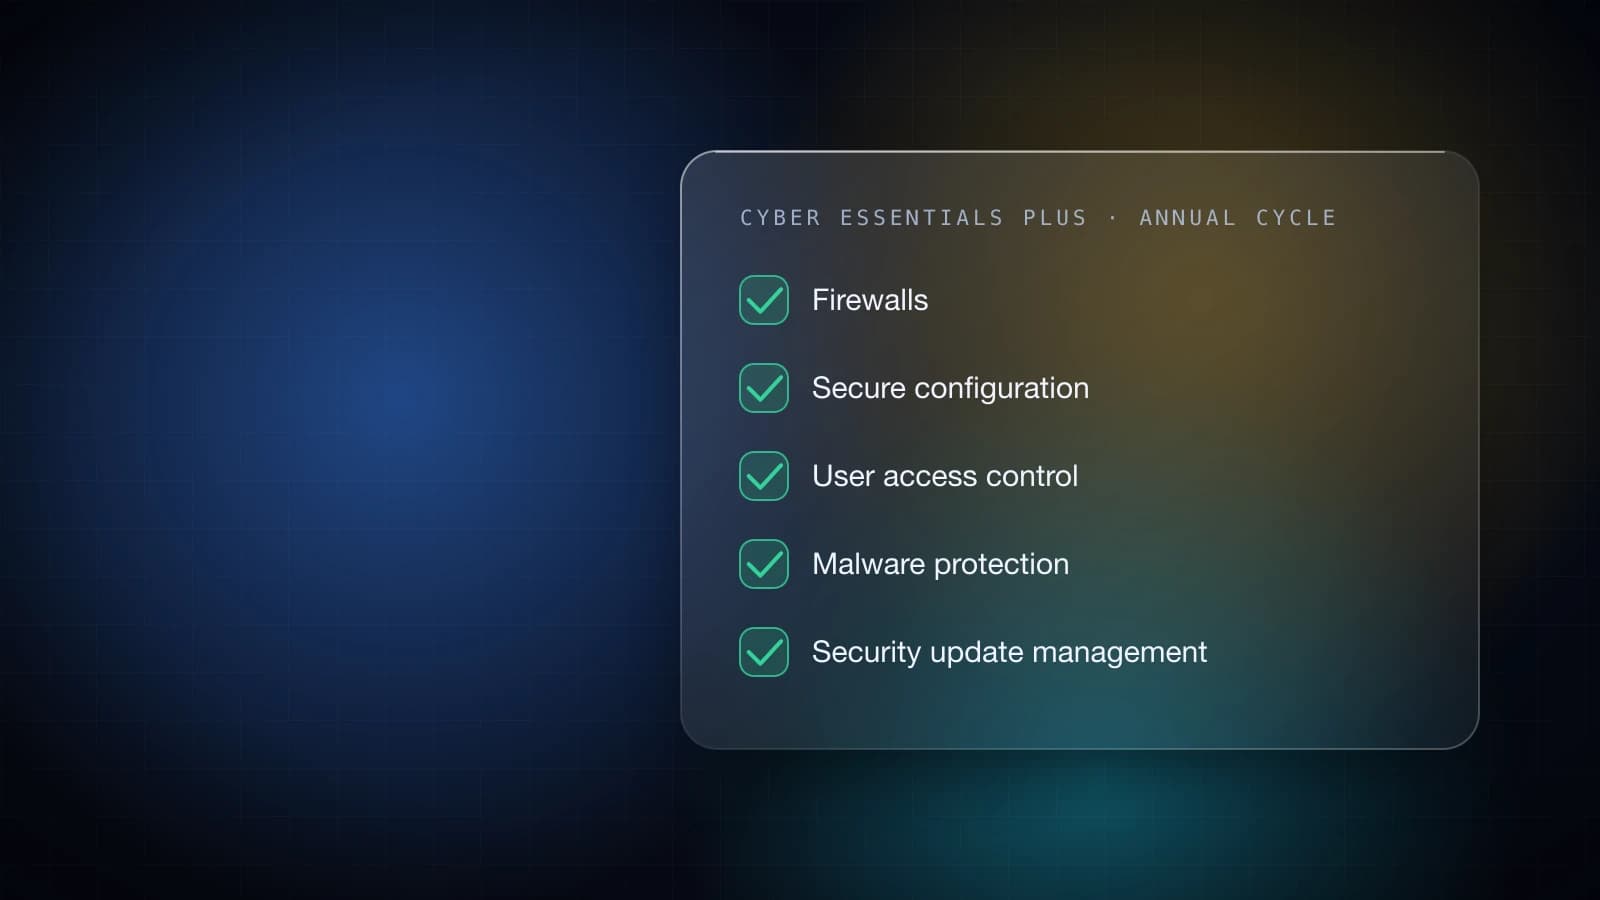
Preparing the organisation for Cyber Essentials Plus certification, running the annual penetration testing programme, and keeping security policy, BCP/DR and awareness training aligned with ISO 27001 and GDPR.
EchoCare: a digital complaint management system for home care

EchoCare: a digital complaint management system for home care

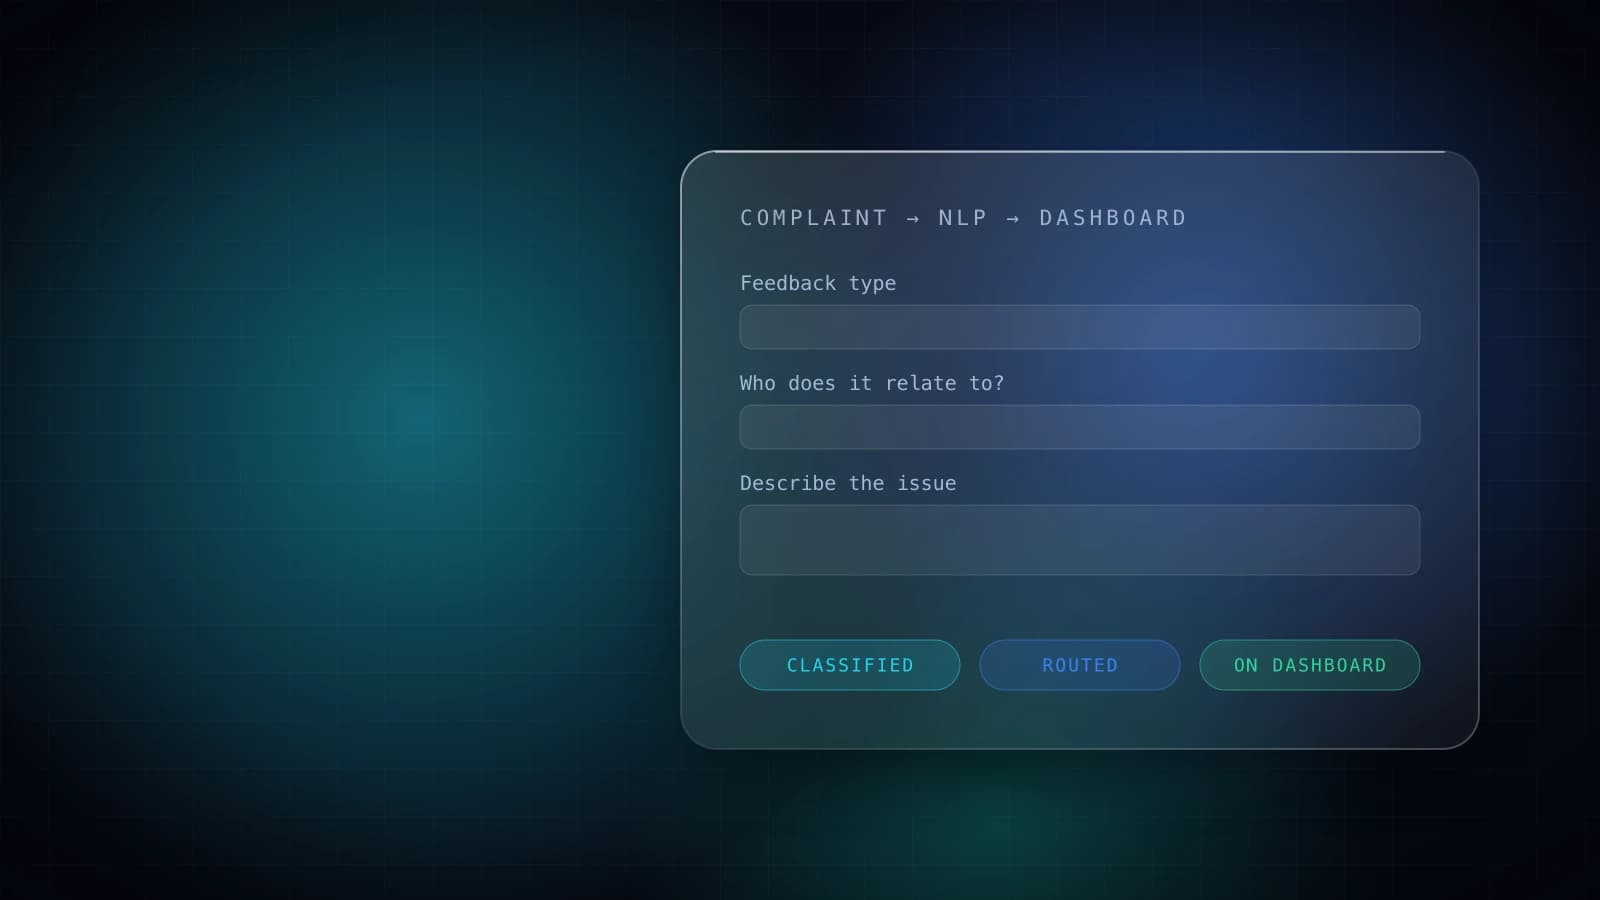
An Innovate UK funded feasibility study and proof of concept with PBL Care Limited and Birmingham City University. The system replaces paper-based complaint handling with CQC-standard digital forms, NLP classification, and a live dashboard.