At a glance
- Organisation: a UK health-tech company handling regulated health data
- My role: led the review, the vendor evaluation, the recommendation, and the rollout
- Estate: endpoints across Windows, macOS, and Linux, plus cloud workloads
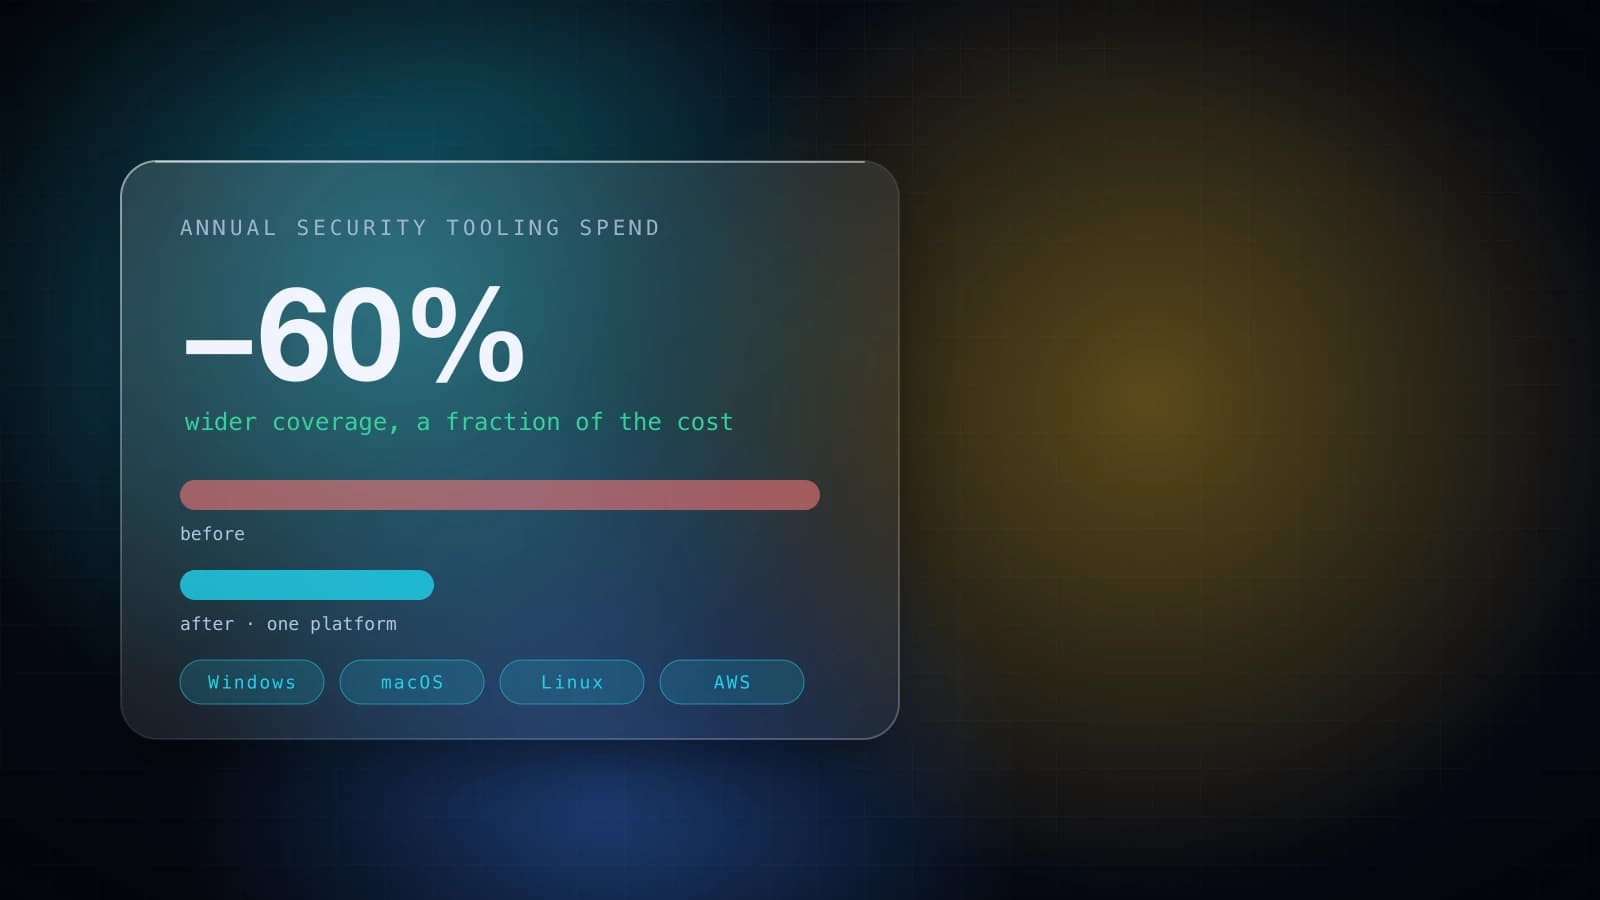
- Result: around 60% lower annual security tooling spend, with wider coverage than before
The problem
How I approached it
- Mapped what we actually had to protect: every operating system in the estate and the cloud environment, rather than starting from vendor feature lists.
- Set the requirements the replacement had to meet:
- native protection for Windows, macOS, and Linux
- cloud-native security for our workloads
- detection and response the team could run day to day
- a total annual cost that made sense for an organisation of our size
- Researched the market and liaised with several vendors, comparing each against those requirements rather than against each other's marketing.
- Recommended one platform that met all the requirements, and ran the migration.
The trade-off
Results
- Around 60% saved every year on security tooling
- One platform covering every operating system in the estate, plus the cloud
- Continuous patching and vulnerability remediation, closing the one gap consolidation left
- A simpler day-to-day operation for the team, with fewer consoles to watch